How State & Local Agencies Use ServiceNow GRC to Meet Compliance Mandates
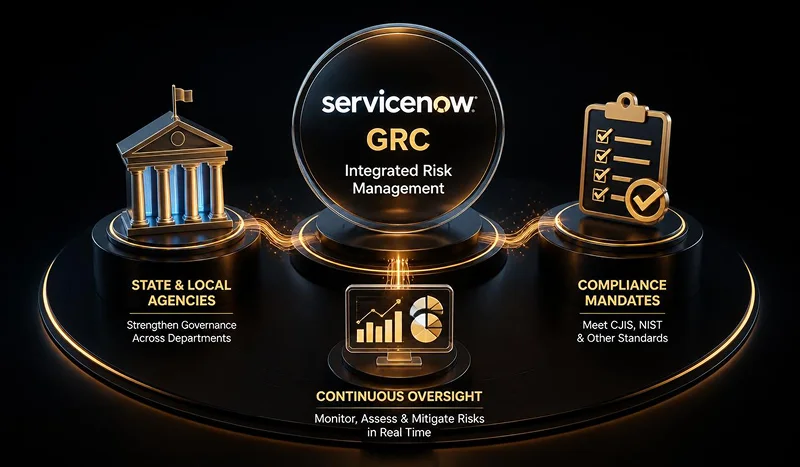
State and local government organizations operate under a complex, ever-shifting web of regulatory expectations. From protecting sensitive law enforcement records under CJIS standards to securing citizen data against cyber threats using NIST guidelines, public sector leaders face continuous scrutiny. However, many municipalities and state departments still rely on manual spreadsheets, fragmented email attachments, and ad-hoc checklists to track their security controls and operational risks.
When compliance tracking relies on manual processes, the risk of human error increases, audit preparation becomes chaotic, and non-compliance penalties loom large.
Understanding
how state & local agencies use ServiceNow GRC to meet compliance mandates offers public sector leaders a clear roadmap toward automated risk oversight. By replacing isolated compliance efforts with a single, continuous monitoring platform, government bodies can protect public trust, streamline federal audits, and improve overall operational resilience.
In this strategic guide, we explore the compliance challenges unique to state and local governments, how ServiceNow Governance, Risk, and Compliance (GRC / Integrated Risk Management) simplifies oversight, and the key benefits of automating public sector governance.
The Public Sector Compliance Reality: High Stakes and Manual Silos
Unlike private enterprises that focus primarily on shareholder value, state and local agencies manage essential public infrastructure, public health programs, and emergency services. A compliance breach or security failure in government carries severe consequences, including interrupted public services, legal exposure, and broken public trust.
Why Legacy Oversight Models Fail Modern Government
Many state departments operate in functional silos—transportation, health services, public safety, and tax administration each managing their own IT assets and compliance documentation independently. This fragmented structure creates significant operational challenges:
- Audit Fatigue: Preparing for annual state or federal audits forces agency staff to spend weeks manually pulling data, hunting down policy attestations, and organizing evidence files across departments.
- Invisible Control Gaps: When an IT security control breaks down in one department (such as an unpatched server or an unverified user permission), agency leadership often has no centralized visibility until an external auditor flags the violation.
- Overwhelming Mandate Overlap: Government entities must comply with multiple overlapping frameworks simultaneously (e.g., NIST SP 800-53, CJIS, HIPAA, IRS Publication 1075, and PCI-DSS). Managing these mandates in isolation leads to duplicated work and wasted administrative hours.
Modernizing Public Sector Oversight with ServiceNow GRC
ServiceNow Governance, Risk, and Compliance (also known as Integrated Risk Management) transforms how government agencies approach regulatory demands. Instead of treating compliance as a once-a-year scramble, the platform embeds continuous monitoring directly into daily operational workflows.
Unifying Policy, Risk, and Audit Management
By building GRC directly on top of the Now Platform, agencies connect risk assessments directly to their real-time IT infrastructure, configuration items (CIs), and service management processes.
Key Capabilities Driving Public Sector Compliance
- Unified Authority Document Mapping: ServiceNow enables agencies to map a single internal security control across multiple regulatory frameworks simultaneously. If a control satisfies both NIST and CJIS requirements, testing it once updates compliance status across both mandates automatically.
- Continuous Control Monitoring: Rather than assuming controls are working between audit cycles, ServiceNow automatically checks system configurations and alerts security teams the moment a compliance baseline fails.
- Automated Evidence Collection: When auditors request proof of compliance, the platform pulls system logs, change request approvals, and user access reviews automatically, eliminating manual document gathering.
- Vendor and Third-Party Risk Oversight: State and local agencies rely heavily on external contractors and cloud vendors. ServiceNow evaluates third-party security postures automatically, protecting agency networks from supply chain vulnerabilities.
Real-World Impact: How Agencies Transform Operations
Adopting automated GRC solutions delivers immediate, tangible benefits for state and local government leadership, operational teams, and citizens alike.
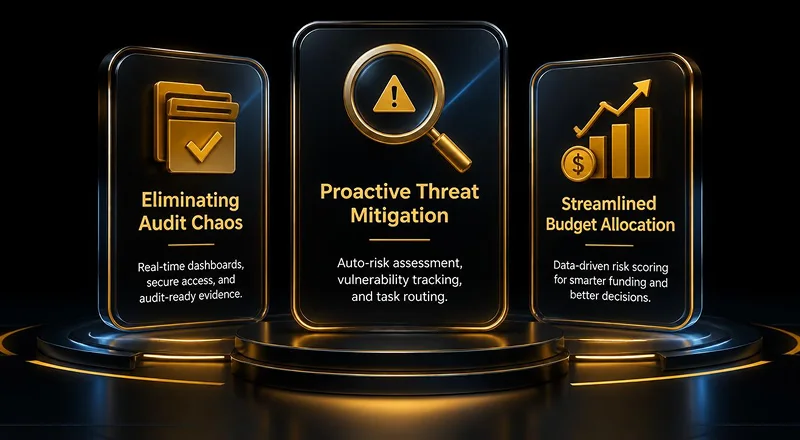
Eliminating Audit Chaos
When state auditors arrive, agency staff no longer need to spend weeks gathering physical records or compiling spreadsheets. Auditors receive secure, role-based access to interactive dashboards showing real-time control status, historical evidence trails, and active remediation plans.
Proactive Threat and Vulnerability Mitigation
By linking GRC directly with ServiceNow Security Operations (SecOps), security teams can automatically assess the compliance impact of a newly discovered system vulnerability. If a high-priority server hosting public records misses a security patch, the system automatically opens a risk assessment task and routes it to the correct engineering group.
Streamlined Budget Allocation
Clear risk scoring helps agency directors justify budget requests to state legislatures or city councils. Instead of asking for general funding, leaders can present data-driven dashboards highlighting specific regulatory risks and the exact investments required to mitigate them.
Key Takeaways
- Break Down Operational Silos: Centralize compliance tracking across public safety, health, and administrative departments into a single source of truth.
- Test Once, Satisfy Many: Cross-map internal security controls across multiple mandates like NIST, CJIS, and HIPAA to eliminate redundant work.
- Shift to Continuous Monitoring: Replace periodic manual audits with automated control checks that flag security gaps in real time.
- Simplify Audit Reporting: Collect compliance evidence automatically, drastically reducing staff effort during regulatory reviews.
Strengthen Your Agency’s Compliance Posture with Mirroar
Modernizing public sector governance requires careful planning, framework mapping, and deep technical experience across the ServiceNow ecosystem. Establishing an automated risk and compliance model is vital for protecting public assets, ensuring regulatory compliance, and maintaining citizen confidence.
At Mirroar, we help state and local government agencies design, implement, and scale ServiceNow GRC solutions built to satisfy strict public sector standards.
Ready to simplify regulatory audits and automate compliance tracking across your agency? Connect with our public sector advisory team at Mirroar today to schedule a comprehensive GRC assessment.